Author: Ken McConkey

  • NDA Essentials, Part 3: The Four Exclusions, and Whose Job It Is to Prove Them

    NDA Essentials, Part 3: The Four Exclusions, and Whose Job It Is to Prove Them

    Two years from now, a competitor ships something that looks a lot like what you shared with them in a conference room, under an NDA that expired a year ago. Nobody is going to fight about whether the NDA existed. They’re going to fight about whether what shipped came from your disclosure or from the other side’s own engineering, and the paragraph that decides that fight is the one almost nobody negotiates: the exclusions.

    The bottom line: the four standard exclusions exist so a recipient isn’t stuck treating its own prior knowledge, or plain public information, as somehow restricted. Whether they’re present in your NDA isn’t the negotiation. Whether your NDA says who has to prove one applies is, and on that question courts don’t agree with each other, which means your contract needs to answer it instead of leaving it to whichever judge you end up in front of.

    Part 1 of this series named these four exclusions among the nine provisions that actually get negotiated. This post is the deeper look, plus the fight nobody sees coming until they’re already in it.

    The Four Carve-Outs, and Where Each One Actually Fails

    Every NDA I’ve reviewed uses some version of the same four. Say them out loud and they sound uncontroversial: you’re not liable for information that was already public, that you already knew, that came to you honestly from someone else, or that you built yourself without touching what was disclosed. Each one fails in a specific, predictable spot.

    Already Public

    Through no fault of the recipient is the phrase doing the work here, and it needs to survive in every version you sign. Drop it and a recipient could leak your information itself and then claim the exclusion, because the information is now, in fact, public. I’ve seen forms shorten this sentence by cutting exactly that phrase. Don’t let it happen to yours.

    Already Known

    This one lives or dies on paper that predates the NDA, not memory. “We already had this” is a sentence anyone can say two years into a dispute, and it’s worth exactly nothing without a business record, an email, a file with a modification date, something dated before the disclosure. Keep the kind of dated record Part 2 recommended for oral disclosures. It does double duty here.

    From a Third Party

    The recipient should have to reasonably believe the third party had the right to disclose the information, not just point to a third party who happened to hand it over. A supplier who breached its own NDA with your counterparty shouldn’t hand your counterparty a clean defense merely by being the source. Push for language that requires the recipient to have no reason to know of a restriction, not language that asks nothing of the recipient at all.

    Independently Developed

    This is the one that actually gets litigated, and it’s the one I’ll spend the rest of this post on.

    Compelled Disclosure Still Isn’t a Fifth Exclusion

    Part 1 of this series flagged this, and it’s worth restating because forms keep getting it wrong: a subpoena or a regulatory demand belongs in its own provision, not bolted onto the exclusions as a fifth carve-out. The difference matters more than it looks. An exclusion removes information from protection permanently, against everyone. A compelled-disclosure clause authorizes one specific disclosure, to one specific requester, while the information stays protected against the rest of the world. Write compelled disclosure as an exclusion, and a single subpoena can read as stripping your trade secret of protection altogether, which is the opposite of what either side actually wants. Structure it instead as prompt notice where notice is lawful, cooperation in seeking protective treatment, and disclosure of no more than the law actually requires. If the disclosure involves an employee or contractor reporting suspected illegal conduct to the government, the Defend Trade Secrets Act’s own whistleblower immunity, 18 U.S.C. § 1833(b)(3), already overrides anything your NDA says regardless. Part 1 has the notice requirement that comes with it.

    The Independent-Development Fight, and Who Has to Prove It

    Every independent-development carve-out I’ve drafted or reviewed uses some version of “without use of or reference to” the disclosed information. Reference to is the clause that should stop you. Use means the recipient actually relied on what it received. Reference to is broader and murkier, close enough to “was aware the information existed while building something similar” that a sufficiently aggressive plaintiff can argue awareness alone defeats the defense, even where the recipient’s engineers never opened the file. I flagged this in Part 1 as one of the two live negotiation points buried in the exclusions, and it’s worth being specific about why: a recipient wants use, full stop, because that’s a standard it can actually meet by running a clean-room process. A discloser wants reference to, because it lowers the bar for a later claim.

    Here’s the part that doesn’t get talked about enough. Even where the contract language is settled, courts don’t agree on who has to prove independent development once a dispute actually lands in front of one of them. The Third Circuit, applying Pennsylvania law in Moore v. Kulicke & Soffa Industries, Inc., 318 F.3d 561 (3d Cir. 2003), held that the burden of persuasion never leaves the party claiming misuse: the recipient only has to offer some evidence of independent development, and the discloser still has to prove that evidence wrong. The Eighth and Ninth Circuits will shift that burden onto the recipient instead. In Garter-Bare Co. v. Munsingwear, Inc., 723 F.2d 707 (9th Cir. 1984), once the discloser showed a confidential relationship and later use of similar information, the recipient had to prove it could have arrived there on its own. Pioneer Hi-Bred International, Inc. v. Holden Foundation Seeds, Inc., 35 F.3d 1226 (8th Cir. 1994), shifted the burden the same way, though the Eighth Circuit tied it to specific facts: the defendant had pursued the plaintiff’s secrets, discarded records that would have shown otherwise, denied obtaining the material, and ended up holding secrets shown to have probably been derived from the discloser’s secrets. Three circuits, two different rules, and in the Eighth Circuit’s case, a rule that depends on facts nobody sorts out until well into the litigation.

    An Example from My Home Jurisdiction, Oklahoma

    The Tenth Circuit recently ruled on a question relevant to this discussion. In Double Eagle Alloys, Inc. v. Hooper, et al., 134 F.4th 1078 (10th Cir. 2025), a Tulsa metals company sued a former employee and the competitor he joined, Ace Alloys, claiming the former employee wrongfully took Double Eagle’s confidential information to his new employer. The Tenth Circuit affirmed summary judgment for the defendants under the Oklahoma Uniform Trade Secrets Act, and a paper trail did the work. Double Eagle lost because it never proved with sufficient evidence that the specifications were secret to begin with: its own website had posted similar numbers, and its customers held nearly identical specs sourced from other suppliers, which the court treated as evidence the information was readily ascertainable through proper means, the same threshold an exclusion never needs to reach if the plaintiff can’t clear it first. Ace Alloys won the independent-development point outright, and won it with a paper trail: “the undisputed evidence also demonstrates that Ace Alloys developed its own … specifications almost a year before [the former employee] even left Double Eagle.” Id. at 1090. A dated engineering file from before the former employee’s departure did more for Ace Alloys than any argument about who had to prove what would have. That’s the fix this post keeps circling back to: whichever exclusion you’re relying on, win it with a record that predates the dispute, not a story assembled after one starts.

    The foregoing split in the Circuit Courts is exactly why leaving this to background law is a bad plan. Your governing-law clause picks a state, not a circuit’s approach to burden-shifting, and you may not know which rule you’re actually going to get until you’re already in the dispute. The fix costs one sentence: state directly in the exclusions provision which side carries the burden of establishing that an exclusion applies, and require that it be established by evidence that predates the disclosure, not by testimony reconstructed after the fact. Something close to “the Receiving Party bears the burden of establishing the applicability of any exclusion under this Section by contemporaneous written evidence” does the job. Whichever side of a given deal you’re usually on, know whether that sentence is doing you a favor or costing you one before you sign it.

    Whose Burden Is It in Your NDA?

    • Confirm your NDA actually says “through no fault of the recipient” on the public-information exclusion, not just “became public.”
    • Check whether your independent-development carve-out uses “use of” or the broader “reference to,” and know which one you want depending on which side of the disclosure you’re usually on.
    • Look for a sentence assigning the burden of proving an exclusion. If there isn’t one, you’re relying on whichever circuit’s rule a court decides applies, and that isn’t a plan.
    • Keep dated records for anything you might need to prove later as prior knowledge or independent development. A file’s timestamp beats a witness’s memory every time.
    • Make sure compelled disclosure lives in its own clause, not folded into the exclusions as a fifth item.

    Part 4 of this series turns to the permitted purpose clause: the one line that decides whether your own ordinary use of what you received counts as a breach.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact Ken McConkey to discuss your company’s specific confidentiality agreements.
  • Who Owns AI-Generated Content? Where U.S. Copyright Law Stands in 2026

    Who Owns AI-Generated Content? Where U.S. Copyright Law Stands in 2026

    Your marketing team produced a quarter’s worth of blog images in an afternoon. Your engineers shipped a feature with an AI coding assistant. Someone rewrote the landing page copy over lunch. Nobody stopped to ask whether you own any of it.

    The bottom line: you probably own less than you think, and what you do own turns entirely on what a human actually contributed. That isn’t a close question anymore, with no split in the U.S. Circuit Courts and the Copyright Office’s own guidance pointing in the same direction. The Supreme Court declined to take it up on March 2, 2026.

    What You Actually Own

    U.S. copyright protects works of human authorship. Material an AI system generates, without meaningful human creative control over its expressive elements, isn’t protected by copyright at all. Not by you, not by the AI vendor, not by the model. It’s unowned from the moment it exists.

    That doesn’t make AI output worthless, and it doesn’t stop you from using it commercially. It means the raw output carries no copyright you can enforce against a competitor who lifts it. Whatever protection you get attaches to the human contribution: the text a person wrote, the edits a person made, the creative selection and arrangement of AI-generated pieces into something larger.

    Looking at Oklahoma law, for example, businesses have no separate state copyright protections. And regardless of which state your business operates in, Copyright is exclusively federal. 17 U.S.C. § 301 preempts state-law rights equivalent to it, though contract, trade secret, and right-of-publicity claims aren’t preempted and can still matter in an AI-content dispute.

    Where the Copyright Office Has Drawn the Line

    The Copyright Office’s refusal letters are more useful than the abstract rule, because they show you the line applied to real facts. Three are worth knowing.

    Zarya of the Dawn. A graphic novel combining the author’s own written text with Midjourney-generated images. The Office split it. The author’s text, and her selection, coordination, and arrangement of the written and visual elements, were registered. The Midjourney-generated images were not, because they were “not the product of human authorship.” Prompts, the Office reasoned, work more like suggestions than orders, since you can’t predict what the system hands back.

    Théâtre D’opéra Spatial. Jason Allen’s award-winning image, refused even though he’d run more than 600 prompts before settling on an output. The problem wasn’t that Allen didn’t work hard enough. It’s that Midjourney “does not interpret prompts as specific instructions to create a particular expressive result.”

    SURYAST. The Copyright applicant fed his own photograph and Van Gogh’s The Starry Night into the AI image generator, then picked a number controlling how strongly thestyle transferred. Copyright refused by the Office. Even with a copyrightable input, the AI system decided where elements landed and what colors applied, and “selecting a single number for a style filter is the kind of de minimis authorship not protected by copyright.”

    The registration guidance itself, published at 88 Fed. Reg. 16190, adds an obligation many people miss. If your work contains more than a de minimis amount of AI-generated material, you have to disclose it and describe what the human contributed. Already registered something without disclosing? File a supplementary registration and correct the record.

    The Framework the Office Applies Now

    In January 2025 the Office published Copyright and Artificial Intelligence, Part 2: Copyrightability. It’s the document your team should be working from, and here is what it says.

    • Prompts alone aren’t enough. “Based on the functioning of current generally available technology, prompts do not alone provide sufficient control.” A longer, more elaborate prompt doesn’t change the analysis, which is worth passing along to anyone on your team convinced their prompt engineering amounts to authorship.
    • Using AI as a tool costs you nothing. “The use of AI tools to assist rather than stand in for human creativity does not affect the availability of copyright protection for the output.” Removing an object from a photo, cleaning up audio: assistive, and fine.
    • Your own expression survives. Feed your copyrightable work in, and whatever of your expression is still perceptible in the result is still yours.
    • Creative selection, coordination, arrangement, and modification of AI material are protectable, as to what the human actually did.

    The Office also declined to recommend new legislation, concluding that “the case has not been made for additional copyright or sui generis protection for AI-generated content.” I’d expect that to hold for a while as Congress has shown no indication of addressing the question, and the Office just spent two years explaining why nothing new is needed.

    Testifying to the Senate Judiciary IP Subcommittee on May 12, 2026, Register of Copyrights Shira Perlmutter said the Office “has to date registered more than 7,000 claims that include AI-generated materials where those materials have been disclaimed.” Works built with AI get registered all the time. They get registered because the applicant disclosed the AI material and claimed only the human part.

    The Courts Agree

    Stephen Thaler applied to register an image naming his AI system as the author. The Office refused. On March 18, 2025, the D.C. Circuit affirmed: “As a matter of statutory law, the Copyright Act requires all work to be authored in the first instance by a human being.” Thaler v. Perlmutter, 130 F.4th 1039 (D.C. Cir. 2025). The reasoning is structural, not philosophical. The Act measures the copyright term by “the life of the author,” passes termination rights to a widow, widower, or surviving children, and requires transfers signed by the owner. None of that works if the author is a machine.

    The line worth keeping is the court’s own caveat: “the human authorship requirement does not prohibit copyrighting work that was made by or with the assistance of artificial intelligence.” Using AI isn’t the disqualifier. Letting AI do the authoring is.

    The Supreme Court denied certiorari on March 2, 2026. Thaler v. Perlmutter, No. 25-449. The same answer had already landed on the patent side, where the Federal Circuit held that an inventor has to be a natural person. Thaler v. Vidal, 43 F.4th 1207 (Fed. Cir. 2022).

    The Part Nobody Has Answered

    Pure AI output isn’t protected. Substantial human authorship is. Where the line falls between those two is still anyone’s guess, and no court has ruled on it.

    Allen v. Perlmutter, No. 1:24-cv-02665 (D. Colo.), is the case to watch. Cross-motions for summary judgment were fully briefed in January 2026 and it’s still pending. It’s the first real chance for a federal court to say how much iterative prompting, curation, and editing adds up to authorship. My guess is the court affirms the Office and says very little about the middle, which would leave everyone roughly where they are now. Worth watching regardless.

    The evidentiary standard is undeveloped too, so nobody knows what proof of human creative contribution a court will want to see. And here’s the one that catches people, a work that isn’t copyrightable can still infringe somebody else’s copyright. Having no protection in your output says nothing about your exposure.

    What a Registrable AI-Assisted Work Looks Like

    Put the negative rules together and a usable path falls out. Nothing about AI in your workflow blocks registration. What blocks it is a deliverable where you can’t point to what the human did.

    The safest version looks like this. A person writes, drafts, photographs, or designs something copyrightable. AI assists somewhere in the process, or generates components. A person then selects among outputs, arranges them, and edits them in ways that add original expression. On the application you claim the human contribution, describe it, and disclaim the AI-generated material. What you get is a registration covering the human layer, which is narrower than a registration covering everything, and considerably better than nothing.

    Zarya of the Dawn is the model here, not the cautionary tale it usually gets cited as. The author walked away with a registration covering her text and her arrangement. She lost the images. That’s the trade, and for most business content it’s a perfectly acceptable one.

    What to Do About It

    Read your AI vendor’s output clause for what it actually says. OpenAI’s consumer Terms of Use, under the Content section, assign you “all our right, title, and interest, if any, in and to Output.” Those two words, “if any,” are doing real work. If the output isn’t copyrightable, the assignment conveys nothing, because there’s nothing to convey. It’s a promise not to claim the material against you, not a warranty that you own it.

    Let me point you to another example in the OpenAI consumer Terms of Use. Look under the Content section at the paragraph titled, “Ownership of content.” It reads, “Due to the nature of our Services and artificial intelligence generally, output may not be unique and other users may receive similar output from our Services. Our assignment above does not extend to other users’ output….” That provision certainly supports another perspective on why you must be vigilant when incorporating AI-generated content into your company’s “hopefully” proprietary assets.

    Assume a competitor can lawfully copy anything you generated purely with AI, or received the same or similar output from their AI tool. That should change what you build with AI and what you don’t. A logo, a mascot, a signature illustration style, anything whose value depends on nobody else being able to use it, needs real human authorship in it, and you need to be able to prove it. Keep the drafts, the prompt histories, the redlines, the version history. Reconstructing that record two years into a dispute is expensive and unconvincing.

    Disclose AI material on registration applications, and do it accurately. A knowing misstatement of material fact can put the registration itself at risk, and the registration is the asset you need in order to sue. Candor costs almost nothing; claim the human contribution, disclaim the rest.

    Fix your IP assignment language. This is the one that occurs most often in SaaS and professional services agreements, and it’s the easiest to miss, because the clause looks fine until you read it against this rule. Most assignment clauses transfer works of authorship the person creates. If your contractor hands you AI output with thin human involvement, there may be no work of authorship to assign, and you’ve paid for a deliverable nobody owns. Address AI-assisted deliverables expressly, add a disclosure obligation, and get a warranty about the human contribution.

    Know whether you’re dealing with an employee or a contractor. Everything above assumes a contractor, because that’s where the assignment clause trap lives. A different rule applies to your own people.

    If your employee creates the work within the scope of employment, and there’s enough human authorship to support a copyright, you own it automatically as a work made for hire under 17 U.S.C. § 201(b). No assignment needed, no signature required. But work made for hire only decides who owns a copyright that already exists. It doesn’t create one. An employee’s purely AI-generated output is exactly as unowned as a contractor’s, work made for hire or not. The question isn’t whose payroll the creator is on. It’s whether a human did enough for there to be a copyright to own.

    One Question to Put to Your Team This Week

    Pick the ten most commercially valuable pieces of content your company produced this year and ask two things about each: did AI make it, and can you prove what the human did? Where the answer runs yes and no, that asset isn’t protected, and any decision you’ve made assuming otherwise needs revisiting.

    The law here is more settled than the headlines suggest. What isn’t settled is the middle, and a ruling out of Colorado could move it one direction or the other before the year is out.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact Ken McConkey to discuss your company’s specific circumstances.

  • NDA Essentials, Part 2: What Counts as Confidential (and the Step Everyone Skips)

    NDA Essentials, Part 2: What Counts as Confidential (and the Step Everyone Skips)

    You said it out loud in a conference room, not in an email. Nobody stamped a document, nobody sent a follow-up memo, and eight months later the relationship went sideways. If your NDA requires written confirmation of anything disclosed orally, that unrecorded conversation may never have been protected at all.

    Part 1 of this series covered nine provisions and gave the definition of confidential information a single paragraph. That undersold it. Everything else in the agreement, the standard of care, the remedies, is arguing about a term the parties often never pinned down. This post covers what actually counts as confidential, why the two standard ways of defining it each fail in their own ways, and the follow-up step almost nobody performs.

    What Actually Gets Called Confidential

    Every definition of confidential information, however it’s worded, is reaching for the same handful of categories:

    • Technical data: source code, architecture documents, product specifications, engineering drawings, algorithms, and features that haven’t shipped yet.
    • Business operations: financials, pricing models, cost structures, strategic plans, and internal processes.
    • Client insights: customer lists, contact information, usage data, and anything that reveals who a company’s customers are or how they use its product.
    • Intellectual property that isn’t yet protected by a patent, copyright registration, or trademark: inventions still in progress, unpatented designs, and plain know-how.

    None of that is where the fight happens. The fight is over how the definition decides whether something you actually said or sent falls into one of these buckets in the first place.

    Two Competing Definitions, and Why Both Fail Alone

    Most NDAs pick one of two approaches to defining confidential information, and each fails in its own way.

    The Marking-Based Definition

    This approach protects only what’s labeled confidential in writing at the time of disclosure, or reduced to a written summary within a set number of days if it wasn’t written to begin with. Clean to apply, and it fails the moment someone forgets, which is often, since nobody marks a Slack message, a shared screen, or a photo of a whiteboard.

    The Catch-All Definition

    This approach instead covers anything a reasonable person would understand to be confidential given the nature of the information and the circumstances of its disclosure. That protects the discloser against exactly the human error above, and it leaves the recipient guessing, in real time, about what it can and can’t use. I’d rather negotiate a longer marking deadline than fight later over what a reasonable person would understand, because that phrase means whatever a judge wants it to.

    Most NDA forms split the difference: marking required for anything written or tangible, a written follow-up required for anything oral or visual. That hybrid is certainly the right idea. But it also creates an obligation almost nobody actually performs.

    The Oral-Disclosure Follow-Up (The One Nobody Performs)

    Here’s the obligation. If your NDA uses the hybrid approach above and you disclose something in a meeting, a demo, or a phone call instead of a document, the agreement typically gives you a window (e.g. 10, 20, sometimes 30 days) to send the other side a written summary identifying what was disclosed and confirming it’s confidential. Miss that window, and under the plain language of most NDA forms, what you talked about in that room was never covered as confidential information.

    This can be more than a mere technicality. It cost a company its trade secret protections in at least one case. In Convolve, Inc. v. Compaq Computer Corp., 527 F. App’x 910 (Fed. Cir. 2013), the NDA required that information disclosed orally or visually be identified as confidential at the time of disclosure and confirmed in a writing delivered within twenty days of the disclosure. Convolve disclosed trade secret information about hard disk drive technology at a meeting and never sent the follow-up confidentiality memo. The Federal Circuit court held the NDA’s language was clear, and rejected Convolve’s argument that both sides understood the information was confidential anyway. A written contract, the court said, supplants whatever informal understanding the parties may have shared. Therefore, what was said in that meeting received no protection under the NDA because its specific provisions were not followed.

    The lesson isn’t that talking is dangerous. It’s that a specific, calendarable obligation is probably sitting in your NDA form right now, and it doesn’t enforce itself. If your form works this way, the fix costs about five minutes after any meeting where you say more than you type; a short email listing what was covered and stating that it’s confidential information under the agreement. Send it before the deadline in your NDA runs.

    The Catch-All Trap

    A definition reading “any and all information disclosed by either party, in any form” looks like maximum protection. It’s closer to the opposite. Courts have pushed back on definitions this broad, especially once they start looking like they restrain a recipient’s ordinary business rather than protect a specific disclosure, and an agreement nobody can actually comply with tends to get read narrowly by a judge deciding what it was reasonable to expect the recipient to do. There’s a practical cost too, not just a legal one. A recipient covering “everything” either ignores the restriction in practice, since no team treats every internal document that touched a vendor conversation as under lock and key, or it locks down so hard that ordinary work grinds to a halt. Either way, the breadth on paper and the reality of how the company actually operates come apart, and that gap is exactly what gets argued over once there’s a dispute.

    The better draft names the categories, technical data, business operations, client insights, unregistered intellectual property, and pairs that with a reasonable marking or written-confirmation mechanism instead of either extreme. It tells your own team what actually needs protecting instead of asking them to guess.

    Which Side of the Table You’re On

    The right structure for this clause depends on which side of the table you’re sitting on more often.

    If You’re Mostly Disclosing

    That’s often still true even when you’re also receiving, in a bidirectional NDA. You want the definition broad enough to cover the ways you actually share information, and you want the marking or follow-up deadline generous enough that your own team can hit it. Thirty days beats ten.

    If You’re Mostly Receiving

    You want the opposite: real categories instead of a catch-all, and a marking or written-confirmation requirement with actual teeth, because that’s what tells you, in the moment, what you’re restricted from doing with what just landed in your inbox or your head. In a mutual NDA you’re negotiating both roles at once, so know which one describes more of your actual dealings with this counterparty before deciding which way to push.

    Before You Sign the Next One

    Pull your current NDA form and check it against this list before the next one lands in your inbox with a signature deadline attached.

    • Match the definition’s categories, technical data, business operations, client insights, intellectual property, to what you’ll actually disclose or receive, not a generic list copied out of a form.
    • If your NDA has a marking requirement, build the habit of stamping documents before they leave the building, not after someone asks.
    • If your NDA allows oral or visual disclosure with a written follow-up window, find that window today and put a five-minute recurring task on your calendar for the day after any substantive meeting with a counterparty.
    • Keep dated records for anything you might need to prove later as prior knowledge or independent development. A file’s modification date is worth more than someone’s memory of who thought of what first.
    • Don’t let a catch-all “everything is confidential” clause substitute for the habits above. Broad language protects you on paper and does nothing for you in a conversation nobody can point back to.
    • Read your current NDA form against this list and note which of these your team is actually equipped to do, not just which ones are already in the document.

    Part 3 of this series turns to the exclusions clause: information already publicly available through no fault of the recipient, information the recipient already knew free of any duty, information from a third party free of any duty, and information independently developed without use of or reference to what was disclosed.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact Ken McConkey to discuss your company’s specific confidentiality agreements.
  • NDA Essentials, Part 1: The Provisions That Actually Get Negotiated

    NDA Essentials, Part 1: The Provisions That Actually Get Negotiated

    The non-disclosure agreement (“NDA”) is the contract most companies sign fastest and read least. It shows up early, it is short, someone calls it standard, and it gets signed so the real negotiation can start. Then, unless you have overriding confidentiality provisions in a later definitive agreement, it governs your business’s confidential information for the next three to five years.

    The takeaway: an NDA is a real contract with real teeth, and about nine provisions in it do all of the work. This discussion covers those nine common provisions at a high level, and each one gets its own post later in this series.

    NDAs come in one of two formats, unidirectional or bidirectional. While it is not unusual to have a vendor or customer provide you with their unidirectional NDA template, I recommend against using such a one-direction NDA unless your business will be disclosing absolutely no confidential information. NDAs in technology and SaaS deals tend to be mutual (bidirectional), as both sides disclose and both sides receive. Every position you take against the other side’s confidential information gets taken against yours, which is why you must stay aware of what restrictions and obligations you are placing on the other party as they are also being placed upon you.

    1. What Counts as Confidential Information

    Two drafting approaches, failing in opposite directions. A marking requirement protects only what is marked as confidential, which is clean on paper and problematic in practice, because people forget to mark a Slack message, a screen share, or a whiteboard photo as confidential. Conversely, a catch-all definition covers anything a reasonable person would understand to be confidential from its nature and the circumstances of disclosure, which protects the discloser and leaves the recipient with no reliable way to know what is restricted.

    2. The Exclusions

    Four carve-outs are standard: information already publicly available through no fault of the recipient, information the recipient already knew free of any duty, information from a third party free of any duty, and information independently developed without use of or reference to what was disclosed. The negotiation is rarely about whether these are present in the NDA. It is about which party carries the burden of proving one of the exclusions, and whether the words “or reference to” survive in the independent-development carve-out.

    Compelled disclosure is where I part company with a lot of forms. A subpoena or regulatory demand often gets drafted as a fifth exclusion, which strips the information of protection the moment a court asks for it. This topic belongs in its own provision as a permitted disclosure: prompt notice where notice is lawful, cooperation in seeking protective treatment, and no more disclosed than the law requires.

    3. The Permitted Purpose

    “Solely to evaluate a potential business relationship between the parties” is one line, and the entire use restriction hangs on it. Draft it too narrowly and your ordinary operations breach the agreement. Draft it too broadly and it’s near unenforceable and useless.

    This clause could matter more than the definition of confidential information and gets a fraction of the attention. The part that is missed by many people is that if the evaluation succeeds and the parties sign an MSA, an NDA limited to evaluating a potential relationship no longer authorizes use of that information to perform the contract. Either the MSA’s confidentiality provision takes over cleanly, or the NDA’s purpose has to cover performance under the later definitive agreement. You must understand the NDA does not exist in a vacuum. It must work with your other agreements. You don’t want conflicting provisions or gaps in coverage.

    4. Who Is Allowed to See Confidential Information

    A need-to-know standard applied to a defined group: employees, affiliates, officers, directors, advisors, contractors, sometimes financing sources. There are two common points of contention; whether affiliates are included and whether those recipients must be bound by written obligations at least as protective as the NDA.

    The provision that makes the rest enforceable is the one making the receiving party responsible for any breach by any party it has communicated your confidential information to, as if it had breached itself. Without it, your remedy could run against an individual contractor instead of the company that handed them the file.

    5. The Standard of Care

    The common standard is reasonable care, and in no event less than the care the recipient uses for its own confidential information of like importance. Both halves matter, because a company with weak internal security has a very low bar for its own information.

    There is a reason to care beyond the contract. State law tends to define trade secrets by the methods used to protect them from public disclosure. For example, information qualifies as a trade secret under the Oklahoma Uniform Trade Secrets Act only if it is “the subject of efforts that are reasonable under the circumstances to maintain its secrecy,” 78 Oklahoma Statutes § 86(4)(b). Your NDAs, and your actual practice under them, are much of what proves that element later. A confidentiality program that exists only in your contract file is not evidence of much.

    6. Two Time Components: Term and Duration

    These are different time components, and confusing them is one of the most common errors in short-form NDAs. The “term” dictates how long new disclosures are covered. The “duration” controls how long the recipient has to protect what was already disclosed. A two-year term with a three-to-five-year survival period is common.

    What commonly gets left out is the trade secret carve-out: obligations as to trade secrets continue for as long as the information remains a trade secret under applicable law. Without a specific trade secret carve-out, a fixed expiration date in your NDA reads as your own agreement that trade secret protection ends on a date certain, an awkward position to hold while arguing you made reasonable efforts to maintain secrecy.

    8. Remedies and Injunctive Relief

    Nearly every NDA states that breach will cause irreparable harm for which money damages are inadequate, and that the disclosing party may obtain injunctive relief without posting a bond. Keep the clause. But do not rely on it as some courts have ruled that where parties have contractually agreed that any breach would constitute irreparable harm, that stipulation without more is insufficient to support an irreparable harm finding. See Dominion Video Satellite, Inc. v. EchoStar Satellite Corp., 356 F.3d 1256 (10th Cir. 2004).

    The damages disclaimer is also worth your consideration. If your NDA waives indirect, incidental, and consequential damages, look hard at what is left, because loss from disclosure of confidential information is very often exactly the category just waived. Accept a broad waiver, lose your injunction, and you are holding an agreement with no effective remedy in it.

    9. The Residual Clause

    Most common in enterprise and SaaS forms, and the provision people are most likely to sign without reading. A residuals clause lets the receiving party use information retained in the unaided memory of individuals who had authorized access. In a technical evaluation, that covers a great deal.

    It is not automatically unacceptable, and it is sometimes necessary, since you cannot ask an engineer to forget an architecture. If you accept one, narrow it: unaided memory only, no intentional memorization, no license under any patent or copyright, no use to develop a competing product, and customer data, pricing, and source code excluded outright.

    Also Worth Thinking About

    • No license, no warranty as to accuracy or completeness, and no obligation to proceed with any transaction. Three sentences that keep an evaluation from turning into an implied deal.
    • The Defend Trade Secrets Act notice, 18 U.S.C. § 1833(b)(3), when the agreement is with an employee or an individual contractor. Omit it and you cannot recover exemplary damages or attorney fees under the DTSA against that person.
    • Governing law and venue, which decide how much the nine provisions above are actually worth to you.

    The Fastest Way to Get This Wrong

    Sign the counterparty’s form because it is only four pages. Length has nothing to do with risk here. Four pages that give away your permitted purpose, your remedies, and your residuals will cost you more than forty pages of a well-built MSA. Read your own template against these nine provisions and find out which side of each one you are on.

    Part 2 of this series will discuss the definition of confidential information: marking requirements, catch-all standards, the oral-disclosure follow-up nobody actually performs, and how to write a definition your own team can follow.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact Ken McConkey to discuss your company’s specific confidentiality agreements.
  • The CTA Saga Ends (For Now): FinCEN Formally Exempts U.S. Companies from Beneficial Ownership Reporting

    The CTA Saga Ends (For Now): FinCEN Formally Exempts U.S. Companies from Beneficial Ownership Reporting

    I’ve written about the Corporate Transparency Act’s (“CTA”) on-again, off-again beneficial ownership reporting requirement twice before on this blog, first chronicling the injunction whiplash of early 2025, then the requirement’s brief return that spring. On August 11, 2026, the U.S. Department of the Treasury’s Financial Crimes Enforcement Network (“FinCEN”) issued a final rule that appears to close the book on that saga, at least for the overwhelming majority of U.S. business owners. The bottom line: if your company was formed under U.S. law, you and your business are no longer required to report beneficial ownership information (“BOI”) to FinCEN under the CTA, and FinCEN says it will delete what you already reported. See also the FAQ issued by FinCEN regarding its Final Rule.

    What the Final Rule Actually Does

    The final rule, published in the Federal Register on August 14, 2026, permanently exempts all domestic reporting companies, meaning any entity formed by filing with a U.S. state or tribal authority, from CTA beneficial ownership reporting. It also exempts U.S. persons from BOI reporting obligations when they are beneficial owners or company applicants of foreign reporting companies, and it eliminates the requirement that U.S. persons holding a FinCEN identifier keep that information updated. FinCEN says it will purge previously filed U.S. person data from its BOI database in a single sweep to be completed by February 10, 2027, with no request required on your part. Foreign entities, meaning companies formed under another country’s law that register to do business in a U.S. state, are the one group still on the hook. They must continue reporting BOI, but now only for their non-U.S. beneficial owners.

    Where This Leaves the Saga

    If you’ve followed my earlier posts on this topic (see The CTA Saga Continues and The CTA is back, and it’s here to help), you’ll recall the CTA’s implementation bounced between competing federal court injunctions, a Supreme Court stay, and a scramble to hit a moving filing deadline, all inside about six weeks in early 2025. FinCEN issued an interim final rule in March 2025 that already exempted most domestic companies as a practical matter. This August 2026 rule makes that exemption permanent and formal, closes remaining gaps such as company applicants and FinCEN ID updates, and directs the wholesale deletion of the data FinCEN already collected. For nearly all U.S. business owners, this is the end of the road on CTA compliance, not another chapter.

    Why FinCEN Is Doing This

    FinCEN’s stated authority for the exemption comes from the CTA itself, specifically the Treasury Secretary’s power under 31 U.S.C. § 5336(a)(11)(B)(xxiv) to exempt any entity or class of entities where BOI collection would not serve the public interest or would not be highly useful to law enforcement. In the rule’s preamble, Treasury points to the CTA’s own directive to minimize the burden on legitimate small businesses, and frames the change as a reassessment following Executive Order 14192’s broader deregulatory push.

    What This Means for Your Business

    If your company was formed in the U.S., you have nothing further to file, and no follow-up action is required on your part. Nobody needs to request deletion of previously filed information; FinCEN says that will happen automatically. If your company was formed outside the U.S. and is registered to do business in a U.S. state, confirm with your corporate counsel whether you still qualify for an exemption and, if not, make sure your BOI filing reports only your non-U.S. beneficial owners. If you’re holding a FinCEN identifier as a U.S. person, you no longer need to keep that information current.

    The Potential Pitfall: Don’t File This Away Completely

    A few things are worth keeping in mind before you treat CTA compliance as permanently closed. First, this relief comes from Treasury’s exemptive authority under the statute, not from Congress repealing the CTA. The underlying law is still on the books, which means a future administration could revisit the exemption through the same rulemaking process. Second, the CTA’s constitutionality is still being litigated, with multiple cases pending and a group of states urging the Supreme Court to take up the question, so the legal landscape here is not fully settled. Third, and this one catches business owners off guard, some states and the District of Columbia have their own, independent beneficial ownership disclosure requirements that operate regardless of anything FinCEN does. Washington, D.C., for example, has required beneficial ownership information from entities formed or registered to do business there since 2020, a requirement the District’s government has confirmed is unaffected by the federal rule change. New York’s LLC Transparency Act, by contrast, was narrowed at the last minute to reach only foreign LLCs registered in New York, so it now largely mirrors the federal approach rather than adding a separate burden on domestic companies. A handful of other states have floated their own beneficial ownership bills, though none has the reach of DC’s law today. The point is that federal relief does not automatically mean you’re off the hook everywhere, so it is worth confirming whether any state or jurisdiction where your company is formed or registered has its own separate requirement. Finally, FinCEN has signaled it may expand the existing Customer Due Diligence Rule that applies to banks, which could mean your bank still asks you for beneficial ownership information when you open or maintain an account, separate and apart from any CTA obligation.
    For most U.S. business owners, this is genuinely good news and a real reduction in compliance burden after a rocky rollout. But “permanent” in an agency rule is not the same as “permanent” in a statute, and entities still filing, along with anyone relying on a state law exemption, should keep an eye on developments. If you’re not sure whether your company still has a CTA obligation, whether a state or local law reaches you, or what your bank may still ask of you, that’s worth a quick conversation before you assume you’re done.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact ME to discuss your specific situation.

  • MSA, SOW, or Both? Structuring SaaS Commercial Contracts Correctly

    MSA, SOW, or Both? Structuring SaaS Commercial Contracts Correctly

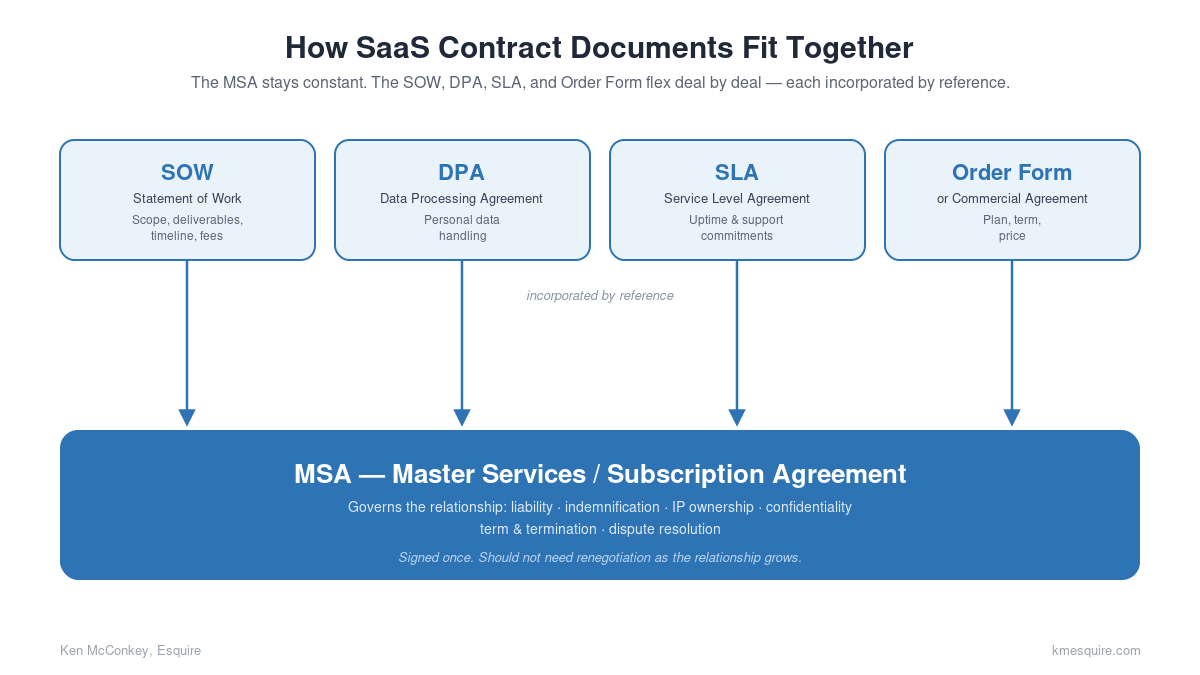
    Most SaaS companies eventually end up with some combination of a Master Services or Subscription Agreement (“MSA”) and a Statement of Work (“SOW”), often without ever deciding on purpose which document is supposed to do what. That usually happens by accident: an early customer needed a signed contract fast, so a single document covered everything, and each deal since has been a variation on that first one. It works until it doesn’t, usually right when a dispute or a new professional-services engagement exposes the gaps. Some companies call the SOW an Order Form or Commercial Agreement. Still others designate an SOW for professional services only and use a separate Order Form or Commercial Agreement for product purchases or subscriptions. For simplicity, this post uses “SOW” to refer to all of these documents, regardless of what your company calls them.

    What an MSA Actually Does

    The MSA is the overall governing document for the relationship. It sets the terms that should stay constant across every engagement with a given customer: limitation of liability, indemnification, intellectual property ownership and license grants, confidentiality, term and termination, and terms dictating how disputes get resolved. It also incorporates or references other supporting documents that carry the operational detail, typically a Data Processing Agreement (“DPA”) for personal data handling and a Service Level Agreement (“SLA”) for uptime and support commitments. Once an MSA is signed, it should not need to be renegotiated every time the relationship changes (i.e. additional services/products are added, or a subscription is renewed, etc.).

    What an SOW Actually Does

    The SOW carries the deal-specific detail: scope of work, deliverables, timeline, fees, and any engagement-specific assumptions or acceptance criteria. A well-drafted SOW does not restate liability caps, indemnification, or IP ownership; it incorporates the MSA by reference and leaves those terms where they belong. That separation is what lets a SaaS company add a new project, a new module, or a new phase of implementation without reopening the entire contract.

    When You Need Both

    If the product involves a recurring subscription plus periodic professional services, onboarding, custom integration work, implementation, or training, you need both documents. The MSA governs the relationship and the risk allocation; each SOW governs a discrete piece of work under that umbrella. This structure lets you sign a new SOW in days instead of weeks, because the terms that actually take time to negotiate are already settled.

    When a Single Order Form Is Enough

    Not every deal needs a freestanding SOW. A self-serve subscription with no custom implementation or professional services can often be handled with an MSA plus a short order form specifying the plan, term, and price. Reserve the full SOW structure for engagements that involve actual scoped work, deliverables, or a project timeline.

    Where SaaS Companies Typically Get Tripped Up

    Three recurring problems show up again and again:

    1. An SOW that includes its own liability or indemnification language that conflicts with the MSA, creating ambiguity about which terms actually control.
    2. An SOW signed for an early pilot or proof of concept with no MSA in place at all, so there is no governing framework once the relationship expands.
    3. No order-of-precedence clause specifying which document controls if the MSA and an SOW conflict, which turns a drafting oversight into a battle of contracts with no clearly stated winner. Most well-drafted MSAs default to the MSA controlling unless the SOW expressly says otherwise, so state that default in your own template rather than leaving it for a judge to decide.

    A Note on Execution

    All 50 states are covered by the federal ESIGN Act, and each state also has its own laws recognizing electronic signatures and records as legally effective, so executing MSAs and SOWs through AdobeSign, DocuSign or a similar platform is enforceable. However, that is not a substitute for good contract structure. A clean order-of-precedence clause and clear incorporation-by-reference language matter regardless of how the documents get signed.

    A Practical Starting Point

    Review your current templates for three things: a clear order-of-precedence clause, proper incorporation of the DPA and SLA by reference rather than restating their terms, and a standard SOW template that pulls its liability and IP terms from the MSA rather than reinventing them each time. Getting this structure right once saves renegotiation on every deal after.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact ME to discuss your company’s specific contract structure.

  • AI vs. Bots vs. Assistants vs. Agents: What Business Owners Should Know

    AI vs. Bots vs. Assistants vs. Agents: What Business Owners Should Know

    “AI,” “bot,” “assistant,” and “agent” get used interchangeably in most business conversations, and that’s costing companies real clarity when they decide what to actually deploy.

    Here’s the plain-language version:

    AI is the underlying technology, the algorithms and data that let software learn, reason, and recognize patterns. It’s the brain, not a product you install.

    Bots are narrow, task-specific tools built to automate one job well: a website chat window answering FAQs, a script that files data, a crawler that indexes pages. Efficient, but limited to what they were built to do.

    Assistants sit a level up. They’re built on AI, understand natural language, hold context across a conversation, and connect into your other tools and workflows, drafting a document, checking a calendar, summarizing a contract. But an assistant still waits for you to ask, one step at a time.

    Agents go a step further. Give an agent a goal, and it plans and carries out a multi-step task on its own, chaining actions and pulling in other tools without waiting for a prompt at each step. An assistant waits for you to ask; an agent runs the workflow itself. Gartner treats assistants as the precursor to agents, not the same thing, and has a name for the common mistake of blurring the two: “agentwashing,” marketing a tool as an agent when it isn’t actually autonomous.

    Why this distinction matters for your business, not just semantics:

    • Gartner projects that 40% of enterprise applications will carry task-specific AI agents, the autonomous, multi-step version of these tools, by the end of 2026, up from under 5% a year earlier. That’s a fast shift from “AI as add-on” to “AI as infrastructure.”
    • A Harvard Business School and BCG field study found knowledge workers using AI on tasks within its strengths worked over 25% faster and produced work rated more than 40% higher in quality, but were also more likely to get it wrong on tasks outside that zone.

    The takeaway: AI tools are not interchangeable, and neither is the level of trust you should place in their output. A bot is right for high-volume, predictable work. An assistant earns its keep on workflow and coordination. An agent earns its keep by taking a multi-step task off your plate entirely. And every one of them still needs a human checking the tasks that fall outside what the tool is actually good at.

    Before your business rolls out the next AI tool, get clear on which of these four you’re actually buying, and what job it’s suited for. What’s your team using AI for right now: automating a task, assisting a workflow, or letting an agent run it end to end?

    Ken McConkey is an attorney in Oklahoma City focusing on SaaS and technology commercial contracts, entity formation and governance, and data privacy compliance. He is Of Counsel to Derryberry & Naifeh, LLP. This Post is general information about legal and business developments, not legal advice, and it does not create an attorney-client relationship.


    Sources

    Gartner: 40% of Enterprise Apps Will Feature Task-Specific AI Agents by 2026 (press release, Aug. 2025).

    Gartner: Agentic AI — Autonomy Is Coming, Are You Ready to Control It? (gartner.com, definitions of AI agent, agentic AI, and “agentwashing”)

    Navigating the Jagged Technological Frontier — Harvard Business School AI Institute / BCG field study

  • LLC vs. S-Corp: What New Founders Get Wrong

    LLC vs. S-Corp: What New Founders Get Wrong

    Almost every new business owner asks the same question early on: should I form a limited liability company (“LLC”) or an S-corporation (also called an “S-Corp”)? The honest answer is that the question itself is usually based on a misunderstanding. Generally speaking, and without reference to any particular state’s or federal law, the law does not create a separate business entity called an S-Corp. Whereas an LLC is a business entity type, S-Corp is not. What people actually need to choose between is a business entity type, such as an LLC, and a tax election, S-Corp in this discussion, that can be layered on top of that entity once it has been formed.

    LLC and S-Corp Aren’t Actually Alternatives

    Under every U.S. state’s law, an LLC is a state law entity formed by filing an organizational document with whatever state agency is specified under that state’s law. In Oklahoma, for example, LLCs are governed under the Oklahoma Limited Liability Company Act, 18 Oklahoma Statutes §§ 2000, et seq., and Articles of Organization are filed with the Oklahoma Secretary of State under that Act. Each state’s law is unique with respect to formation and administration of LLCs, and the organizational document goes by different names depending on the state (Articles of Organization, Certificate of Formation, Certificate of Organization, and so on). An S-corporation, by contrast, is not a state entity at all. It is a federal tax classification under Subchapter S of the Internal Revenue Code, elected by filing IRS Form 2553. You can form an LLC in any state and separately elect to have it taxed as an S-corporation for federal purposes. The LLC and the S-Corp election operate on entirely different legal layers, which is why “LLC vs. S-Corp” is a slightly misleading way to frame the decision.

    What Founders Are Actually Deciding

    The real decisions are twofold: what state law entity to form (often an LLC for a new small business, given its flexibility and liability protection), and how that entity should be taxed, either as a default disregarded entity or partnership, or by S-corporation election. There are many factors to weigh in choosing your business’s tax election, which is why it is worth including your corporate counsel and accountant in that discussion. One factor often considered is that the S-Corp election generally becomes worth exploring once the business is consistently profitable enough that the owner is paying meaningful self-employment tax on profits beyond a reasonable salary, since S-Corp status allows profits above that salary to avoid self-employment tax. The right threshold varies by business, but founders often start seriously considering it once net profit is consistently well above what a reasonable salary for the owner’s role would be.

    A Note on S-Corp Elections: Federal vs. State Law

    LLCs default to one of two federal tax classifications if no further election is filed with the IRS: disregarded entity or partnership. The details and exceptions can matter, but generally speaking, a single-member LLC defaults to a disregarded entity for federal income tax purposes, and an LLC with two or more members defaults to a partnership. If you want to deviate from that default classification, specifically to elect S-corporation tax treatment, you can timely file IRS Form 2553, provided you meet the S-Corp election requirements. Both the timing and the eligibility requirements matter, and each is summarized below.

    Legally, a business entity electing S-Corp tax classification remains whatever entity type it was formed as (an LLC, in this discussion). Eligibility for the S-Corp election is governed by federal tax rules, not state entity law: no more than 100 shareholders, shareholders generally must be individuals, and only one class of stock, among other requirements. States also do not uniformly follow the federal S-Corp election. Some states, Oklahoma among them, recognize the federal election automatically at the state level, while others require a separate state-level election, and a few impose an entity-level tax on S-Corps despite the federal pass-through treatment. State treatment is worth confirming before you rely on any assumption about pass-through taxation.

    What the S-Corp Election Actually Requires

    Electing S-Corp status is not a one-time decision with no ongoing obligations. It requires running the owner as a W-2 employee at a reasonable salary, which means payroll, payroll tax filings, and more bookkeeping formality than a default LLC. Many states, Oklahoma included, generally follow the federal S-Corp tax treatment for state income tax purposes, but the added payroll administration is real and ongoing, not a one-time filing. The S-Corp election allows the owner to be paid a reasonable salary while treating a portion of the remaining net profits as distributions, avoiding payroll tax on that portion, but the split must be structured reasonably to avoid running afoul of the Internal Revenue Code. The election also provides pass-through taxation, meaning the entity itself generally does not pay tax at the federal level the way a traditional corporation might, though some states allow an entity-level election of their own that can be beneficial in certain situations. Understanding your full range of options, and structuring the business in the most tax-advantageous way available within the law, matters here. The goal is reasonable tax avoidance, which is legal, not tax evasion, which is not.

    Formation Costs and Practical Next Steps

    Formation fees vary by state. An Oklahoma LLC, for example, currently costs $100 to file Articles of Organization with the Secretary of State (roughly $104 if filing online), plus a $25 annual certificate fee each year to stay in good standing. The federal S-Corp election itself, filing IRS Form 2553, carries no separate filing fee, but budget for the added cost of running payroll if you make the election. The right sequence for most new founders is to form the LLC first with the right governance documents in place, operate for a period, and revisit the S-Corp election once profitability makes the payroll administration worth the tax benefit. If you have already decided, after appropriate due diligence, that you want S-Corp tax status from the outset, IRS Form 2553 generally must be filed no more than two months and fifteen days after the entity’s formation date. A different deadline applies if the business has no prior tax year, so confirm the specific filing window with your corporate counsel or accountant before relying on it.

    Getting the entity and the tax election right from the start avoids a more expensive cleanup later. If you’re deciding how to structure a new business, that’s a conversation worth having before you file anything.

    This post is provided for general informational purposes only and does not constitute legal advice or tax advice. Reading this post does not create an attorney-client relationship. Contact ME about your specific situation.

  • Paying for ChatGPT or Claude Doesn’t Make Your Business Data Confidential

    Paying for ChatGPT or Claude Doesn’t Make Your Business Data Confidential

    A growing number of business owners run day-to-day work, drafting emails, summarizing contracts, brainstorming strategy, through a paid AI subscription, and assume that because they’re paying, their conversations are private. That assumption is often wrong. Consumer-paid plans like ChatGPT Plus or Pro, Claude Pro or Max, and Gemini Advanced buy you speed, higher limits, and better models than the free tiers, but they remain consumer products governed by individual terms of service and privacy policies, not the enterprise contracts that come with real confidentiality guarantees.

    This post covers general business confidentiality. It doesn’t address the separate, more demanding duty attorneys owe under the rules of professional conduct, that’s a different discussion for another day. If you’re a lawyer, the short version is: do not put client information into a free or consumer-tier AI tool. And to be clear, nothing here is a recommendation of one platform over another; each has its own strengths, and this is simply a look at what their policies actually say.

    Are Your Prompts and Responses Actually Confidential?

    Not completely. Your prompts and the model’s responses are processed and stored on the provider’s own systems, not end-to-end encrypted the way a secure messaging app is. Providers retain data for operational, safety, legal, and, depending on your settings, model-improvement purposes. Consumer paid plans don’t come with the contractual protections, a data processing agreement, zero-data-retention options, audit rights, that commercial and enterprise tiers typically include. Treating a paid consumer chat as a private notebook is a real risk for client data, employee or customer personal information, or anything covered by an NDA or a regulatory obligation.

    Will Your Conversations Be Used to Train the Model?

    This is where the platforms diverge most, and it’s worth checking your own account settings rather than assuming.

    • OpenAI (ChatGPT, including Plus): the default is on. Your conversations may be used to train future models unless you turn off “Improve the model for everyone” under Settings, Data Controls. Temporary Chats are never used for training and are deleted after 30 days regardless. Business, Enterprise, Team, and Edu plans include additional controls and generally exclude customer data from training by default.
    • Anthropic (Claude Free, Pro, Max): the default is off. Anthropic only uses your chats to improve Claude if you affirmatively turn that setting on in Privacy Settings, with one exception: conversations flagged by Anthropic’s safety systems can still be analyzed to improve abuse detection regardless of your setting. Incognito chats are excluded from training even when the general setting is on. Feedback submitted through the thumbs up or down button is retained for up to five years and may be used regardless of your training preference. Claude for Work and API accounts don’t train on customer content by default.
    • Google (Gemini, including Advanced): controlled by the “Keep Activity” setting. When it’s on, your chats, and Gemini Live audio, video, or screenshares, may be used to improve Google’s AI models, with your activity auto-deleted after 18 months by default (adjustable). When it’s off, chats aren’t used for training, but Google still retains them for 72 hours to operate the service and guard against abuse, and submitting feedback can bring part of that conversation back into scope for review.

    Across all three, an opt-out, or a decision not to opt in, is forward-looking only. Data already folded into a completed training run can’t be pulled back out after the fact.

    Can a Human Actually Read What You Typed?

    Yes, in a limited way, on every platform. A restricted set of employees or contractors can review flagged or sampled conversations to investigate abuse, respond to a support request you initiated, handle legal process, or check response quality when training and improvement settings are enabled. Google is explicit that a subset of chats go through human review to improve its models and keep the platform safe, and that reviewed conversations are retained separately for up to three years, even after you delete your own activity history. None of the major platforms promise that no human will ever see a given conversation; they promise that access is limited, logged, and tied to a specific business reason.

    What This Means for Your Business.

    A paid subscription buys you capability, faster responses, higher limits, stronger models, not enterprise-grade confidentiality. If your team is putting anything sensitive into an AI tool, contract terms, financial data, employee information, unreleased product details, the safer path is an approved commercial or enterprise account whose contract actually restricts training and human access, backed by an internal policy that keeps that kind of information off personal accounts.

    Even on a consumer plan, you can meaningfully cut your exposure:

    • Turn off the model-improvement or training setting, and use Temporary, Incognito, or “Keep Activity off” modes where available.
    • Keep confidential, personal, or regulated data out of the tool entirely.
    • Review and delete chat history on a regular schedule.
    • Check the current settings and policy language for the specific plan your team actually uses, these terms change, and the version that matters is the one attached to your account today.

    Policies on all three platforms have shifted meaningfully over the past year, and they’ll shift again. The summary above reflects each provider’s stated policy as of this writing; the only reliable source going forward is the terms and privacy settings tied to your own account.

    This post is provided for general informational purposes only and does not constitute legal advice. It does not address the separate confidentiality obligations attorneys owe under the rules of professional conduct. Reading this post does not create an attorney-client relationship. Contact ME to discuss your company’s specific circumstances.

  • Data Privacy Compliance for SaaS Companies Selling Across State Lines

    Data Privacy Compliance for SaaS Companies Selling Across State Lines

    If your SaaS company sells to customers in more than one state, and most do by design, you are likely already subject to more than one state’s privacy law, whether or not your company is headquartered in that state. What began with California’s Consumer Privacy Act (“CCPA”) has grown into a patchwork of approximately twenty (20) comprehensive state privacy laws, with more states adopting similar frameworks each year. This year alone Indiana, Kentucky, and Rhode Island joined the list. For SaaS companies, “we’re not based there” is no longer a reliable answer to “do we have to comply there.”

    Why Your Home State Doesn’t Determine Your Obligations

    Most state privacy laws apply based on where your customers or users are located, and how much of their personal data you process, not where your company is incorporated or headquartered. A SaaS company based in Oklahoma serving customers in California, Colorado, Virginia, Connecticut, and a dozen other states can find itself subject to all of those states’ requirements simultaneously. It’s a bit of a compliance nightmare right now with little hope for a unified federal data privacy law coming to tame the masses. As for current state laws, applicability thresholds vary (some laws apply based on revenue, others based on the number of residents’ records processed), so the analysis has to be done state by state.

    The Common Threads Across State Laws

    Despite the patchwork, most comprehensive state privacy laws share a core set of requirements: consumers get rights to access, correct, delete, and in some cases port their personal data; consumers can opt out of the sale of personal data and certain targeted advertising; companies must maintain reasonable data security safeguards; and companies must have data processing agreements in place with vendors and subprocessors who touch personal data on their behalf. If your SaaS product already has a privacy policy and a standard Data Processing Agreement (“DPA”) in its commercial contract stack, you have a foundation. The question is whether that foundation actually reflects the specific obligations that apply to your current customer footprint.

    Where SaaS Companies Typically Get Tripped Up

    Three recurring gaps show up again and again: DPAs that were drafted years ago and never updated to reflect current state law requirements or the company’s current subprocessor list; privacy policies that describe data practices in the abstract but don’t actually match what the product does today; and no internal process for tracking which states trigger new obligations as the customer base grows, so compliance becomes reactive instead of built in.

    A Practical Starting Point

    Before assuming you need a state-by-state legal opinion for every jurisdiction, most SaaS companies benefit from three concrete steps: mapping what personal data the product actually collects and where it flows, including subprocessors; reviewing the current DPA and privacy policy against that map; and building a lightweight internal process to flag new state obligations as the customer base expands. From there, targeted legal review can focus on the states and data types that create the most real exposure, rather than trying to solve every jurisdiction at once.
    Multi-state privacy compliance is manageable when it’s built into how a SaaS company already reviews and negotiates its commercial contracts, rather than treated as a separate project. If your DPA or privacy policy hasn’t been reviewed against your current customer footprint, that’s a good place to start the conversation.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact ME to discuss your company’s specific circumstances.