Category: SaaS Agreements

  • NDA Essentials, Part 5: Who Can See Your Confidential Information, and Who Answers for Them

    NDA Essentials, Part 5: Who Can See Your Confidential Information, and Who Answers for Them

    You sign an NDA with a company’s U.S. subsidiary. The NDA lets the subsidiary share your information with its “Affiliates,” so the German parent company gets a look. When you ask whether the parent should sign its own NDA, one of its people tells you not to bother, because everyone is already covered. A year later the talks are dead, and you believe the parent is trying to build your product on its own. You sue the parent for breaching the NDA. You lose, because the parent never signed it.

    That’s close to what happened in Knight Capital Partners Corp. v. Henkel AG & Co., KGaA, 930 F.3d 775 (6th Cir. 2019).

    The bottom line: the recipients clause in your NDA answers two questions. Who on the other side may see your information, and who you can hold responsible when one of them misuses it. The answer to the second is usually the company that signed and nobody else, so the clause has to make that company answer for everyone it shares with.

    Part 1 of this series covered this provision in two short paragraphs, and Part 4 promised the longer version. Here it is.

    Two Lists and a Sentence

    The first list says who counts, usually through a defined term, “Representatives,” covering some mix of affiliates, directors, officers, employees, agents, advisors, contractors, and sometimes financing sources. The second list says what has to be true before any of them sees anything: a need to know for the permitted purpose, notice that the information is confidential, and, in better drafts, written confidentiality obligations at least as protective as the NDA.

    Then comes the sentence that matters most when something goes wrong: the receiving party is responsible for any breach by its Representatives.

    Recipients usually want the first list long and the second one short. Disclosers want the reverse. The responsibility sentence is where both sides should slow down, and Knight Capital shows why.

    The Affiliate Who Could See Everything and Signed Nothing

    Knight Capital Partners (“KCP”) was set up to broker a distribution deal for a novel citrus-based cleaning product. In 2014 it signed an NDA with Henkel Corporation, the U.S. subsidiary of Germany’s Henkel AG & Co., KGaA. The NDA let Henkel Corporation share KCP’s information with its “Affiliates,” defined to include any entity that controlled it, which put the German parent squarely inside the definition. Any affiliate that received information became a “Receiving Party,” limited to using it for the purpose of the NDA.

    The deal never happened. KCP sued only the parent, claiming it used KCP’s information to try to develop the product itself. A parent company employee told KCP’s CEO that no second NDA was needed because they were covered by the one already signed, and he later testified that he was bound by the NDA as an affiliate.

    The Sixth Circuit, applying Connecticut law under the NDA’s choice-of-law clause, held that none of it made the parent a party. Only parties are liable for breach of contract. The NDA named KCP and Henkel Corporation as the parties, only they signed it, and it gave affiliates a role as recipients without making them contracting parties. The court read the parent’s “we’re bound” statements as reaffirming its obligations as a Receiving Party, not as joining the contract.

    For a discloser, the lesson is simple: the company that signs is the company you’ll sue, so make it answer for every recipient as if each breach were its own. If one affiliate matters more than the rest, like a parent with its own product development group, ask that affiliate to sign a joinder or the NDA itself.

    Contractors, Vendors, and the Word “Agents”: An Oklahoma Example

    In CMI Roadbuilding, Inc. v. SpecSys, Inc., No. CIV-18-1245-G, 2021 WL 2189222 (W.D. Okla. May 28, 2021), CMI hired SpecSys to manufacture mobile equipment and provide engineering services. Their NDA let SpecSys share CMI’s information with “Representatives” who needed to know it, had been given a copy of the NDA, and had agreed to be bound by the same or similar terms. “Representatives” meant SpecSys’s directors, officers, employees, agents, or advisors.

    SpecSys sent CMI’s engineering documents to at least four parts vendors. CMI called that an unauthorized disclosure. SpecSys said the vendors were its agents or advisors, and that CMI had authorized the disclosures anyway through a letter it gave SpecSys for buying CMI’s proprietary components. Judge Goodwin wrote that the vendors arguably qualified as agents or advisors, declined to decide that contract question without real argument from either side, and found genuine fact disputes on both points. CMI’s own position was that it didn’t object to drawings going to vendors that already had NDAs with CMI.

    This is an unreported trial-court order, and it decided nothing about what “agents” means. That’s the point. Both companies plainly expected vendors to see the drawings, their recipients list didn’t say so, and more than two years into the lawsuit a federal judge couldn’t tell from the contract who was allowed to see what.

    SaaS deals are full of the same people: the offshore development shop, the implementation partner, the contract engineer, the hosting provider. Most of them aren’t anyone’s “agent” in the legal sense. If you’re receiving, name the categories you’ll actually use. If you’re disclosing, decide which ones you’re comfortable with and say so. And if your team plans to paste the other side’s information into an AI tool, ask whether that tool’s vendor is on the list at all.

    Affiliates and Financing Sources Need Their Own Lines

    “Affiliates” is usually defined by control, so a recipient with a large corporate family can share your information with entities you’ve never heard of, including some that compete with you. A blanket affiliate grant is likely overbroad. Limit it to controlled affiliates, named affiliates, or affiliates that need the information for the deal, and keep the signing party responsible for all of them.

    Financing sources come up mostly in acquisitions, where sellers worry that a buyer’s equity co-investor is really another bidder. As an example, the New York City Bar’s model NDA keeps equity sources out unless the seller consents in writing. That default works for commercial deals too: anyone outside the agreed categories sees nothing without your written consent.

    The Statutes Help, but Only So Far

    If the information is a trade secret, a downstream recipient may have statutory exposure without signing anything. Under the Oklahoma Uniform Trade Secrets Act, disclosing or using a trade secret without consent is misappropriation when the person knew or had reason to know it was “derived from or through a person who owed a duty to the person seeking relief to maintain its secrecy or limit its use.” 78 Oklahoma Statutes § 86(2)(b)(2)(c). The federal Defend Trade Secrets Act uses nearly identical language. 18 U.S.C. § 1839(5)(B)(ii)(III).

    That’s a narrower path than a contract claim. You have to prove the information is a trade secret, which much of what an NDA covers isn’t, and prove what the recipient knew. Trade secret status also depends on “efforts that are reasonable under the circumstances to maintain its secrecy,” 78 Oklahoma Statutes § 86(4)(b), and a court weighing those efforts will want to know who you let see the information and on what terms. A tight recipients list helps you there too.

    Who’s on Your List?

    • Find the definition that controls who may receive. It may be “Representatives,” or it may be folded into the definition of “Receiving Party,” as it was in Knight Capital.
    • If you’re receiving, add the categories you actually use: contractors, subcontractors, implementation partners, specific affiliates. Don’t rely on “agents.”
    • If you’re disclosing, require a need to know, notice of confidentiality, and written obligations at least as protective as the NDA, plus your written consent for anyone outside the list.
    • Find the responsibility sentence, and add one if it’s missing. Expect a recipient to ask that it apply only where the recipient failed to use reasonable care in choosing and supervising the person. Decide in advance whether you’ll accept that.
    • If one affiliate matters more than the others, get its signature on a joinder or on the NDA itself.
    • Keep a dated list of who received what. It’s the record Part 4 recommended, with names added.

    Something close to this handles most of that list: “The Receiving Party may disclose Confidential Information only to those of its and its controlled Affiliates’ directors, officers, employees, contractors, and professional advisors who need to know it for the Purpose, have been told its confidential nature, and are bound by written confidentiality obligations at least as protective as this Agreement. The Receiving Party is responsible for any act or omission of any person to whom it discloses Confidential Information that would breach this Agreement if done by the Receiving Party.” If you usually receive, check those categories against how your company actually works before you sign.

    Part 6 of this series turns to the standard of care: what “reasonable care” requires of the recipient, and why the recipient’s own security practices end up setting the floor.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact Ken McConkey to discuss your company’s specific confidentiality agreements.
  • NDA Essentials, Part 4: The Permitted Purpose Clause, Where Too Narrow and Too Broad Both Cost You

    NDA Essentials, Part 4: The Permitted Purpose Clause, Where Too Narrow and Too Broad Both Cost You

    You signed an NDA so two companies could talk about a possible deal. The deal happened, the relationship ran for about two years, and then one side attached the other’s confidential audit report to a federal lawsuit. Was that a breach of the NDA? An Idaho court said no, because the NDA covered a possible relationship and by then the relationship was real. One sentence in the contract, the permitted purpose, decided the outcome.

    The bottom line: the permitted purpose is the use restriction in your NDA, and it cuts both ways. Draft it too narrowly and the deal itself, or your ordinary business, can fall outside it. Draft it too broadly and the other side can do nearly anything with what you gave them. This post covers both sides of the table.

    Part 3 of the NDA Essentials series closed by calling this the one line that decides whether your own ordinary use of what you received counts as a breach. It decides the reverse question just as often: whether what the other side did with your information was allowed.

    Why One Sentence Does So Much Work

    Most NDAs say the recipient may use confidential information solely to evaluate a potential relationship. Everything else in the NDA gets measured against that purpose.

    The law leans on it too. Under the Oklahoma Uniform Trade Secrets Act, using a trade secret without consent is misappropriation when the user knew the information was acquired “under circumstances giving rise to a duty to maintain its secrecy or limit its use.” 78 Oklahoma Statutes § 86(2)(b)(2)(b). The federal Defend Trade Secrets Act uses nearly identical language. 18 U.S.C. § 1839(5)(B)(ii)(II). The purpose clause is how an NDA creates that duty to limit use, and it also defines consent. Use inside the purpose is consented to. Use outside it isn’t.

    Courts start with the words you wrote. Oklahoma law gives effect to a contract’s language when it is clear and explicit, 15 Oklahoma Statutes § 154, and reads the whole contract together so each clause helps interpret the others, 15 Oklahoma Statutes § 157. A judge deciding what your purpose clause allowed isn’t going to ask what you meant when you signed.

    Too Narrow: The Protection That Ended When the Deal Began

    In Dickinson Frozen Foods, Inc. v. J.R. Simplot Co., 434 P.3d 1275 (Idaho 2019), Simplot faced a potato shred shortage in August 2014 and signed an NDA with a frozen foods processor it was considering as a supplier (“DFF”). The NDA limited use of the processor’s information to discussions about a “possible” vendor relationship. The two companies then did a deal. At some point after the parties had entered into the deal, DFF shared a confidential audit report with Simplot. About two years later, Simplot attached DFF’s confidential audit report to a federal complaint in a separate dispute, and a copy of the complaint later reached a lender. The Idaho Supreme Court held that was not a breach. The NDA covered a “possible relationship,” and once the parties entered an actual one they were no longer discussing a possible one. The court also rejected the argument that the NDA’s three-year confidentiality period kept the report protected, and noted that any ambiguity would be read against DFF, which had drafted the NDA.

    Idaho may not be your state, and this decision doesn’t bind anyone outside of Idaho. But Oklahoma starts from the same place, the words on the page, and your state may as well. So if your state also starts with the language in the NDA, I wouldn’t bet on a court there reading “possible” more generously.

    Part 1 of the NDA Essentials series stated the recipient’s version of this point: an NDA limited to evaluation doesn’t authorize using the information to later perform the contract. Dickinson is the discloser’s version. The same too-narrow wording that leaves a recipient exposed can leave the discloser unprotected. If your NDA is likely to turn into an MSA, say so in the purpose: evaluate, negotiate, and, if the parties sign a definitive agreement, perform it. Then make sure the MSA’s confidentiality clause covers what was shared before signing and says whether it replaces the NDA, because a broad entire-agreement clause can quietly do exactly that. My post on MSAs, SOWs, or both covers how those documents fit together.

    Too Broad: When “Evaluate” Includes Deciding to Build It Yourself

    The opposite problem showed up in Olaplex, Inc. v. L’Oréal USA, Inc., 855 F. App’x 701 (Fed. Cir. 2021). In 2015, L’Oréal explored buying Olaplex and signed an NDA that barred any use of Olaplex’s confidential information “other than to evaluate, negotiate and, if applicable, consummate a possible Transaction.” L’Oréal used Olaplex’s business information in a build-versus-buy analysis, asking whether to acquire the company or develop its own product. Olaplex called that misuse. The Federal Circuit disagreed: the NDA authorized that use, and Olaplex’s own co-founder testified that L’Oréal could use the information that way. Consent defeated the misappropriation theory on that information.

    Olaplex also lost on other grounds, since much of what it called secret was public or too vague. The decision is nonprecedential and applied Delaware trade secret standards, so treat it as an illustration, not a rule. It’s a good one, though. “Evaluate” is a broader word than most founders realize, because evaluating a possible acquisition naturally includes asking whether you’d be better off building the thing yourself. If you’re the discloser, say in the purpose that using the information to decide whether to develop, acquire, or license a competing product isn’t a permitted use. If you’re the recipient, know that the broad reading helps you, and expect the discloser to push back.

    A Tenth Circuit Example, and What the Clause Doesn’t Do for You

    A purpose clause gets you a breach claim. It doesn’t get you damages. In GeoMetWatch Corp. v. Behunin, 38 F.4th 1183 (10th Cir. 2022), a weather-satellite company shared confidential business and technical information with an outside businessman’s company under a Mutual NDA dated November 6, 2013. The recipient agreed not to use the information for any purpose other than facilitating the development and distribution of the company’s systems and services. About six weeks later, the businessman’s group launched a new company, and the satellite company sued. It lost on summary judgment, and the Tenth Circuit, applying Utah law, affirmed. The company had no non-speculative evidence that the defendants’ conduct, rather than its own failure to meet its financing partner’s conditions, caused its losses. In short, the company failed to prove the defendant was the cause of its lost profits damage claim. The court didn’t need to decide what the NDA meant. The case turned on whether the company could prove harm.

    A tight purpose clause makes the breach easy to describe. What it cost you is a separate element of the claim, and the records are the proof: what you shared, when you shared it, and what the other side did next. Part 9 of this series covers remedies.

    Does Pasting It Into an AI Tool Count as Using It for the Purpose?

    Let’s take an AI side trip. Say a recipient’s employee pastes your pricing model into a public AI chatbot to summarize it for an internal meeting. Arguably that serves the purpose. The real problem is where the information goes next, since public tools may retain what’s entered and use it to improve their models. A purpose clause that says nothing about AI leaves you arguing over whether a summarizing tool counts as an evaluation aid.

    A July 2026 Carta Law article and a December 2025 Terms.Law guide land in the same place. Don’t ban “AI” across the board, since it’s built into tools like Microsoft 365, Google Workspace, Zoom, and Slack. Define generative AI, bar using your information to train or fine-tune any model, and allow enterprise tools only when the vendor is contractually barred from training on your data. My earlier post on why paying for ChatGPT or Claude doesn’t make your business data confidential explains why that last condition matters.

    What Does Your Purpose Clause Actually Allow?

    • Find the purpose sentence first. It often sits in the opening paragraph or recitals, not under a use heading.
    • Replace “a business relationship” with what you’re actually doing, and say whether the purpose carries through performance of a definitive agreement.
    • Look at the word “evaluate.” If you’re disclosing, decide whether the other side deciding to build instead is a permitted use. If you’re receiving, decide whether you want that door left open.
    • List what is off limits: developing or improving a competing product, competitive analysis, and training AI models on the information.
    • Check that the MSA’s confidentiality clause covers what was shared before signing, and says whether it replaces the NDA.
    • Keep a dated log of what you shared and what the other side did next.

    Something close to this sentence handles most of that list: “The Receiving Party may use Confidential Information solely to evaluate and negotiate a potential transaction between the parties and, if the parties sign a definitive agreement, to perform its obligations and exercise its rights under it, and for no other purpose, including developing or improving a competing product or service or training any artificial intelligence model.” Whichever side of the table you usually sit on, know whether each phrase in that sentence is working for you or against you before you sign.

    Part 5 of this series turns to who is allowed to see confidential information: the affiliates, advisors, and contractors a recipient can share it with, and who answers if one of them gets it wrong.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact Ken McConkey to discuss your company’s specific confidentiality agreements.
  • NDA Essentials, Part 3: The Four Exclusions, and Whose Job It Is to Prove Them

    NDA Essentials, Part 3: The Four Exclusions, and Whose Job It Is to Prove Them

    Two years from now, a competitor ships something that looks a lot like what you shared with them in a conference room, under an NDA that expired a year ago. Nobody is going to fight about whether the NDA existed. They’re going to fight about whether what shipped came from your disclosure or from the other side’s own engineering, and the paragraph that decides that fight is the one almost nobody negotiates: the exclusions.

    The bottom line: the four standard exclusions exist so a recipient isn’t stuck treating its own prior knowledge, or plain public information, as somehow restricted. Whether they’re present in your NDA isn’t the negotiation. Whether your NDA says who has to prove one applies is, and on that question courts don’t agree with each other, which means your contract needs to answer it instead of leaving it to whichever judge you end up in front of.

    Part 1 of this series named these four exclusions among the nine provisions that actually get negotiated. This post is the deeper look, plus the fight nobody sees coming until they’re already in it.

    The Four Carve-Outs, and Where Each One Actually Fails

    Every NDA I’ve reviewed uses some version of the same four. Say them out loud and they sound uncontroversial: you’re not liable for information that was already public, that you already knew, that came to you honestly from someone else, or that you built yourself without touching what was disclosed. Each one fails in a specific, predictable spot.

    Already Public

    Through no fault of the recipient is the phrase doing the work here, and it needs to survive in every version you sign. Drop it and a recipient could leak your information itself and then claim the exclusion, because the information is now, in fact, public. I’ve seen forms shorten this sentence by cutting exactly that phrase. Don’t let it happen to yours.

    Already Known

    This one lives or dies on paper that predates the NDA, not memory. “We already had this” is a sentence anyone can say two years into a dispute, and it’s worth exactly nothing without a business record, an email, a file with a modification date, something dated before the disclosure. Keep the kind of dated record Part 2 recommended for oral disclosures. It does double duty here.

    From a Third Party

    The recipient should have to reasonably believe the third party had the right to disclose the information, not just point to a third party who happened to hand it over. A supplier who breached its own NDA with your counterparty shouldn’t hand your counterparty a clean defense merely by being the source. Push for language that requires the recipient to have no reason to know of a restriction, not language that asks nothing of the recipient at all.

    Independently Developed

    This is the one that actually gets litigated, and it’s the one I’ll spend the rest of this post on.

    Compelled Disclosure Still Isn’t a Fifth Exclusion

    Part 1 of this series flagged this, and it’s worth restating because forms keep getting it wrong: a subpoena or a regulatory demand belongs in its own provision, not bolted onto the exclusions as a fifth carve-out. The difference matters more than it looks. An exclusion removes information from protection permanently, against everyone. A compelled-disclosure clause authorizes one specific disclosure, to one specific requester, while the information stays protected against the rest of the world. Write compelled disclosure as an exclusion, and a single subpoena can read as stripping your trade secret of protection altogether, which is the opposite of what either side actually wants. Structure it instead as prompt notice where notice is lawful, cooperation in seeking protective treatment, and disclosure of no more than the law actually requires. If the disclosure involves an employee or contractor reporting suspected illegal conduct to the government, the Defend Trade Secrets Act’s own whistleblower immunity, 18 U.S.C. § 1833(b)(3), already overrides anything your NDA says regardless. Part 1 has the notice requirement that comes with it.

    The Independent-Development Fight, and Who Has to Prove It

    Every independent-development carve-out I’ve drafted or reviewed uses some version of “without use of or reference to” the disclosed information. Reference to is the clause that should stop you. Use means the recipient actually relied on what it received. Reference to is broader and murkier, close enough to “was aware the information existed while building something similar” that a sufficiently aggressive plaintiff can argue awareness alone defeats the defense, even where the recipient’s engineers never opened the file. I flagged this in Part 1 as one of the two live negotiation points buried in the exclusions, and it’s worth being specific about why: a recipient wants use, full stop, because that’s a standard it can actually meet by running a clean-room process. A discloser wants reference to, because it lowers the bar for a later claim.

    Here’s the part that doesn’t get talked about enough. Even where the contract language is settled, courts don’t agree on who has to prove independent development once a dispute actually lands in front of one of them. The Third Circuit, applying Pennsylvania law in Moore v. Kulicke & Soffa Industries, Inc., 318 F.3d 561 (3d Cir. 2003), held that the burden of persuasion never leaves the party claiming misuse: the recipient only has to offer some evidence of independent development, and the discloser still has to prove that evidence wrong. The Eighth and Ninth Circuits will shift that burden onto the recipient instead. In Garter-Bare Co. v. Munsingwear, Inc., 723 F.2d 707 (9th Cir. 1984), once the discloser showed a confidential relationship and later use of similar information, the recipient had to prove it could have arrived there on its own. Pioneer Hi-Bred International, Inc. v. Holden Foundation Seeds, Inc., 35 F.3d 1226 (8th Cir. 1994), shifted the burden the same way, though the Eighth Circuit tied it to specific facts: the defendant had pursued the plaintiff’s secrets, discarded records that would have shown otherwise, denied obtaining the material, and ended up holding secrets shown to have probably been derived from the discloser’s secrets. Three circuits, two different rules, and in the Eighth Circuit’s case, a rule that depends on facts nobody sorts out until well into the litigation.

    An Example from My Home Jurisdiction, Oklahoma

    The Tenth Circuit recently ruled on a question relevant to this discussion. In Double Eagle Alloys, Inc. v. Hooper, et al., 134 F.4th 1078 (10th Cir. 2025), a Tulsa metals company sued a former employee and the competitor he joined, Ace Alloys, claiming the former employee wrongfully took Double Eagle’s confidential information to his new employer. The Tenth Circuit affirmed summary judgment for the defendants under the Oklahoma Uniform Trade Secrets Act, and a paper trail did the work. Double Eagle lost because it never proved with sufficient evidence that the specifications were secret to begin with: its own website had posted similar numbers, and its customers held nearly identical specs sourced from other suppliers, which the court treated as evidence the information was readily ascertainable through proper means, the same threshold an exclusion never needs to reach if the plaintiff can’t clear it first. Ace Alloys won the independent-development point outright, and won it with a paper trail: “the undisputed evidence also demonstrates that Ace Alloys developed its own … specifications almost a year before [the former employee] even left Double Eagle.” Id. at 1090. A dated engineering file from before the former employee’s departure did more for Ace Alloys than any argument about who had to prove what would have. That’s the fix this post keeps circling back to: whichever exclusion you’re relying on, win it with a record that predates the dispute, not a story assembled after one starts.

    The foregoing split in the Circuit Courts is exactly why leaving this to background law is a bad plan. Your governing-law clause picks a state, not a circuit’s approach to burden-shifting, and you may not know which rule you’re actually going to get until you’re already in the dispute. The fix costs one sentence: state directly in the exclusions provision which side carries the burden of establishing that an exclusion applies, and require that it be established by evidence that predates the disclosure, not by testimony reconstructed after the fact. Something close to “the Receiving Party bears the burden of establishing the applicability of any exclusion under this Section by contemporaneous written evidence” does the job. Whichever side of a given deal you’re usually on, know whether that sentence is doing you a favor or costing you one before you sign it.

    Whose Burden Is It in Your NDA?

    • Confirm your NDA actually says “through no fault of the recipient” on the public-information exclusion, not just “became public.”
    • Check whether your independent-development carve-out uses “use of” or the broader “reference to,” and know which one you want depending on which side of the disclosure you’re usually on.
    • Look for a sentence assigning the burden of proving an exclusion. If there isn’t one, you’re relying on whichever circuit’s rule a court decides applies, and that isn’t a plan.
    • Keep dated records for anything you might need to prove later as prior knowledge or independent development. A file’s timestamp beats a witness’s memory every time.
    • Make sure compelled disclosure lives in its own clause, not folded into the exclusions as a fifth item.

    Part 4 of this series turns to the permitted purpose clause: the one line that decides whether your own ordinary use of what you received counts as a breach.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact Ken McConkey to discuss your company’s specific confidentiality agreements.
  • NDA Essentials, Part 2: What Counts as Confidential (and the Step Everyone Skips)

    NDA Essentials, Part 2: What Counts as Confidential (and the Step Everyone Skips)

    You said it out loud in a conference room, not in an email. Nobody stamped a document, nobody sent a follow-up memo, and eight months later the relationship went sideways. If your NDA requires written confirmation of anything disclosed orally, that unrecorded conversation may never have been protected at all.

    Part 1 of this series covered nine provisions and gave the definition of confidential information a single paragraph. That undersold it. Everything else in the agreement, the standard of care, the remedies, is arguing about a term the parties often never pinned down. This post covers what actually counts as confidential, why the two standard ways of defining it each fail in their own ways, and the follow-up step almost nobody performs.

    What Actually Gets Called Confidential

    Every definition of confidential information, however it’s worded, is reaching for the same handful of categories:

    • Technical data: source code, architecture documents, product specifications, engineering drawings, algorithms, and features that haven’t shipped yet.
    • Business operations: financials, pricing models, cost structures, strategic plans, and internal processes.
    • Client insights: customer lists, contact information, usage data, and anything that reveals who a company’s customers are or how they use its product.
    • Intellectual property that isn’t yet protected by a patent, copyright registration, or trademark: inventions still in progress, unpatented designs, and plain know-how.

    None of that is where the fight happens. The fight is over how the definition decides whether something you actually said or sent falls into one of these buckets in the first place.

    Two Competing Definitions, and Why Both Fail Alone

    Most NDAs pick one of two approaches to defining confidential information, and each fails in its own way.

    The Marking-Based Definition

    This approach protects only what’s labeled confidential in writing at the time of disclosure, or reduced to a written summary within a set number of days if it wasn’t written to begin with. Clean to apply, and it fails the moment someone forgets, which is often, since nobody marks a Slack message, a shared screen, or a photo of a whiteboard.

    The Catch-All Definition

    This approach instead covers anything a reasonable person would understand to be confidential given the nature of the information and the circumstances of its disclosure. That protects the discloser against exactly the human error above, and it leaves the recipient guessing, in real time, about what it can and can’t use. I’d rather negotiate a longer marking deadline than fight later over what a reasonable person would understand, because that phrase means whatever a judge wants it to.

    Most NDA forms split the difference: marking required for anything written or tangible, a written follow-up required for anything oral or visual. That hybrid is certainly the right idea. But it also creates an obligation almost nobody actually performs.

    The Oral-Disclosure Follow-Up (The One Nobody Performs)

    Here’s the obligation. If your NDA uses the hybrid approach above and you disclose something in a meeting, a demo, or a phone call instead of a document, the agreement typically gives you a window (e.g. 10, 20, sometimes 30 days) to send the other side a written summary identifying what was disclosed and confirming it’s confidential. Miss that window, and under the plain language of most NDA forms, what you talked about in that room was never covered as confidential information.

    This can be more than a mere technicality. It cost a company its trade secret protections in at least one case. In Convolve, Inc. v. Compaq Computer Corp., 527 F. App’x 910 (Fed. Cir. 2013), the NDA required that information disclosed orally or visually be identified as confidential at the time of disclosure and confirmed in a writing delivered within twenty days of the disclosure. Convolve disclosed trade secret information about hard disk drive technology at a meeting and never sent the follow-up confidentiality memo. The Federal Circuit court held the NDA’s language was clear, and rejected Convolve’s argument that both sides understood the information was confidential anyway. A written contract, the court said, supplants whatever informal understanding the parties may have shared. Therefore, what was said in that meeting received no protection under the NDA because its specific provisions were not followed.

    The lesson isn’t that talking is dangerous. It’s that a specific, calendarable obligation is probably sitting in your NDA form right now, and it doesn’t enforce itself. If your form works this way, the fix costs about five minutes after any meeting where you say more than you type; a short email listing what was covered and stating that it’s confidential information under the agreement. Send it before the deadline in your NDA runs.

    The Catch-All Trap

    A definition reading “any and all information disclosed by either party, in any form” looks like maximum protection. It’s closer to the opposite. Courts have pushed back on definitions this broad, especially once they start looking like they restrain a recipient’s ordinary business rather than protect a specific disclosure, and an agreement nobody can actually comply with tends to get read narrowly by a judge deciding what it was reasonable to expect the recipient to do. There’s a practical cost too, not just a legal one. A recipient covering “everything” either ignores the restriction in practice, since no team treats every internal document that touched a vendor conversation as under lock and key, or it locks down so hard that ordinary work grinds to a halt. Either way, the breadth on paper and the reality of how the company actually operates come apart, and that gap is exactly what gets argued over once there’s a dispute.

    The better draft names the categories, technical data, business operations, client insights, unregistered intellectual property, and pairs that with a reasonable marking or written-confirmation mechanism instead of either extreme. It tells your own team what actually needs protecting instead of asking them to guess.

    Which Side of the Table You’re On

    The right structure for this clause depends on which side of the table you’re sitting on more often.

    If You’re Mostly Disclosing

    That’s often still true even when you’re also receiving, in a bidirectional NDA. You want the definition broad enough to cover the ways you actually share information, and you want the marking or follow-up deadline generous enough that your own team can hit it. Thirty days beats ten.

    If You’re Mostly Receiving

    You want the opposite: real categories instead of a catch-all, and a marking or written-confirmation requirement with actual teeth, because that’s what tells you, in the moment, what you’re restricted from doing with what just landed in your inbox or your head. In a mutual NDA you’re negotiating both roles at once, so know which one describes more of your actual dealings with this counterparty before deciding which way to push.

    Before You Sign the Next One

    Pull your current NDA form and check it against this list before the next one lands in your inbox with a signature deadline attached.

    • Match the definition’s categories, technical data, business operations, client insights, intellectual property, to what you’ll actually disclose or receive, not a generic list copied out of a form.
    • If your NDA has a marking requirement, build the habit of stamping documents before they leave the building, not after someone asks.
    • If your NDA allows oral or visual disclosure with a written follow-up window, find that window today and put a five-minute recurring task on your calendar for the day after any substantive meeting with a counterparty.
    • Keep dated records for anything you might need to prove later as prior knowledge or independent development. A file’s modification date is worth more than someone’s memory of who thought of what first.
    • Don’t let a catch-all “everything is confidential” clause substitute for the habits above. Broad language protects you on paper and does nothing for you in a conversation nobody can point back to.
    • Read your current NDA form against this list and note which of these your team is actually equipped to do, not just which ones are already in the document.

    Part 3 of this series turns to the exclusions clause: information already publicly available through no fault of the recipient, information the recipient already knew free of any duty, information from a third party free of any duty, and information independently developed without use of or reference to what was disclosed.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact Ken McConkey to discuss your company’s specific confidentiality agreements.
  • NDA Essentials, Part 1: The Provisions That Actually Get Negotiated

    NDA Essentials, Part 1: The Provisions That Actually Get Negotiated

    The non-disclosure agreement (“NDA”) is the contract most companies sign fastest and read least. It shows up early, it is short, someone calls it standard, and it gets signed so the real negotiation can start. Then, unless you have overriding confidentiality provisions in a later definitive agreement, it governs your business’s confidential information for the next three to five years.

    The takeaway: an NDA is a real contract with real teeth, and about nine provisions in it do all of the work. This discussion covers those nine common provisions at a high level, and each one gets its own post later in this series.

    NDAs come in one of two formats, unidirectional or bidirectional. While it is not unusual to have a vendor or customer provide you with their unidirectional NDA template, I recommend against using such a one-direction NDA unless your business will be disclosing absolutely no confidential information. NDAs in technology and SaaS deals tend to be mutual (bidirectional), as both sides disclose and both sides receive. Every position you take against the other side’s confidential information gets taken against yours, which is why you must stay aware of what restrictions and obligations you are placing on the other party as they are also being placed upon you.

    1. What Counts as Confidential Information

    Two drafting approaches, failing in opposite directions. A marking requirement protects only what is marked as confidential, which is clean on paper and problematic in practice, because people forget to mark a Slack message, a screen share, or a whiteboard photo as confidential. Conversely, a catch-all definition covers anything a reasonable person would understand to be confidential from its nature and the circumstances of disclosure, which protects the discloser and leaves the recipient with no reliable way to know what is restricted.

    2. The Exclusions

    Four carve-outs are standard: information already publicly available through no fault of the recipient, information the recipient already knew free of any duty, information from a third party free of any duty, and information independently developed without use of or reference to what was disclosed. The negotiation is rarely about whether these are present in the NDA. It is about which party carries the burden of proving one of the exclusions, and whether the words “or reference to” survive in the independent-development carve-out.

    Compelled disclosure is where I part company with a lot of forms. A subpoena or regulatory demand often gets drafted as a fifth exclusion, which strips the information of protection the moment a court asks for it. This topic belongs in its own provision as a permitted disclosure: prompt notice where notice is lawful, cooperation in seeking protective treatment, and no more disclosed than the law requires.

    3. The Permitted Purpose

    “Solely to evaluate a potential business relationship between the parties” is one line, and the entire use restriction hangs on it. Draft it too narrowly and your ordinary operations breach the agreement. Draft it too broadly and it’s near unenforceable and useless.

    This clause could matter more than the definition of confidential information and gets a fraction of the attention. The part that is missed by many people is that if the evaluation succeeds and the parties sign an MSA, an NDA limited to evaluating a potential relationship no longer authorizes use of that information to perform the contract. Either the MSA’s confidentiality provision takes over cleanly, or the NDA’s purpose has to cover performance under the later definitive agreement. You must understand the NDA does not exist in a vacuum. It must work with your other agreements. You don’t want conflicting provisions or gaps in coverage.

    4. Who Is Allowed to See Confidential Information

    A need-to-know standard applied to a defined group: employees, affiliates, officers, directors, advisors, contractors, sometimes financing sources. There are two common points of contention; whether affiliates are included and whether those recipients must be bound by written obligations at least as protective as the NDA.

    The provision that makes the rest enforceable is the one making the receiving party responsible for any breach by any party it has communicated your confidential information to, as if it had breached itself. Without it, your remedy could run against an individual contractor instead of the company that handed them the file.

    5. The Standard of Care

    The common standard is reasonable care, and in no event less than the care the recipient uses for its own confidential information of like importance. Both halves matter, because a company with weak internal security has a very low bar for its own information.

    There is a reason to care beyond the contract. State law tends to define trade secrets by the methods used to protect them from public disclosure. For example, information qualifies as a trade secret under the Oklahoma Uniform Trade Secrets Act only if it is “the subject of efforts that are reasonable under the circumstances to maintain its secrecy,” 78 Oklahoma Statutes § 86(4)(b). Your NDAs, and your actual practice under them, are much of what proves that element later. A confidentiality program that exists only in your contract file is not evidence of much.

    6. Two Time Components: Term and Duration

    These are different time components, and confusing them is one of the most common errors in short-form NDAs. The “term” dictates how long new disclosures are covered. The “duration” controls how long the recipient has to protect what was already disclosed. A two-year term with a three-to-five-year survival period is common.

    What commonly gets left out is the trade secret carve-out: obligations as to trade secrets continue for as long as the information remains a trade secret under applicable law. Without a specific trade secret carve-out, a fixed expiration date in your NDA reads as your own agreement that trade secret protection ends on a date certain, an awkward position to hold while arguing you made reasonable efforts to maintain secrecy.

    8. Remedies and Injunctive Relief

    Nearly every NDA states that breach will cause irreparable harm for which money damages are inadequate, and that the disclosing party may obtain injunctive relief without posting a bond. Keep the clause. But do not rely on it as some courts have ruled that where parties have contractually agreed that any breach would constitute irreparable harm, that stipulation without more is insufficient to support an irreparable harm finding. See Dominion Video Satellite, Inc. v. EchoStar Satellite Corp., 356 F.3d 1256 (10th Cir. 2004).

    The damages disclaimer is also worth your consideration. If your NDA waives indirect, incidental, and consequential damages, look hard at what is left, because loss from disclosure of confidential information is very often exactly the category just waived. Accept a broad waiver, lose your injunction, and you are holding an agreement with no effective remedy in it.

    9. The Residual Clause

    Most common in enterprise and SaaS forms, and the provision people are most likely to sign without reading. A residuals clause lets the receiving party use information retained in the unaided memory of individuals who had authorized access. In a technical evaluation, that covers a great deal.

    It is not automatically unacceptable, and it is sometimes necessary, since you cannot ask an engineer to forget an architecture. If you accept one, narrow it: unaided memory only, no intentional memorization, no license under any patent or copyright, no use to develop a competing product, and customer data, pricing, and source code excluded outright.

    Also Worth Thinking About

    • No license, no warranty as to accuracy or completeness, and no obligation to proceed with any transaction. Three sentences that keep an evaluation from turning into an implied deal.
    • The Defend Trade Secrets Act notice, 18 U.S.C. § 1833(b)(3), when the agreement is with an employee or an individual contractor. Omit it and you cannot recover exemplary damages or attorney fees under the DTSA against that person.
    • Governing law and venue, which decide how much the nine provisions above are actually worth to you.

    The Fastest Way to Get This Wrong

    Sign the counterparty’s form because it is only four pages. Length has nothing to do with risk here. Four pages that give away your permitted purpose, your remedies, and your residuals will cost you more than forty pages of a well-built MSA. Read your own template against these nine provisions and find out which side of each one you are on.

    Part 2 of this series will discuss the definition of confidential information: marking requirements, catch-all standards, the oral-disclosure follow-up nobody actually performs, and how to write a definition your own team can follow.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact Ken McConkey to discuss your company’s specific confidentiality agreements.

  • MSA, SOW, or Both? Structuring SaaS Commercial Contracts Correctly

    MSA, SOW, or Both? Structuring SaaS Commercial Contracts Correctly

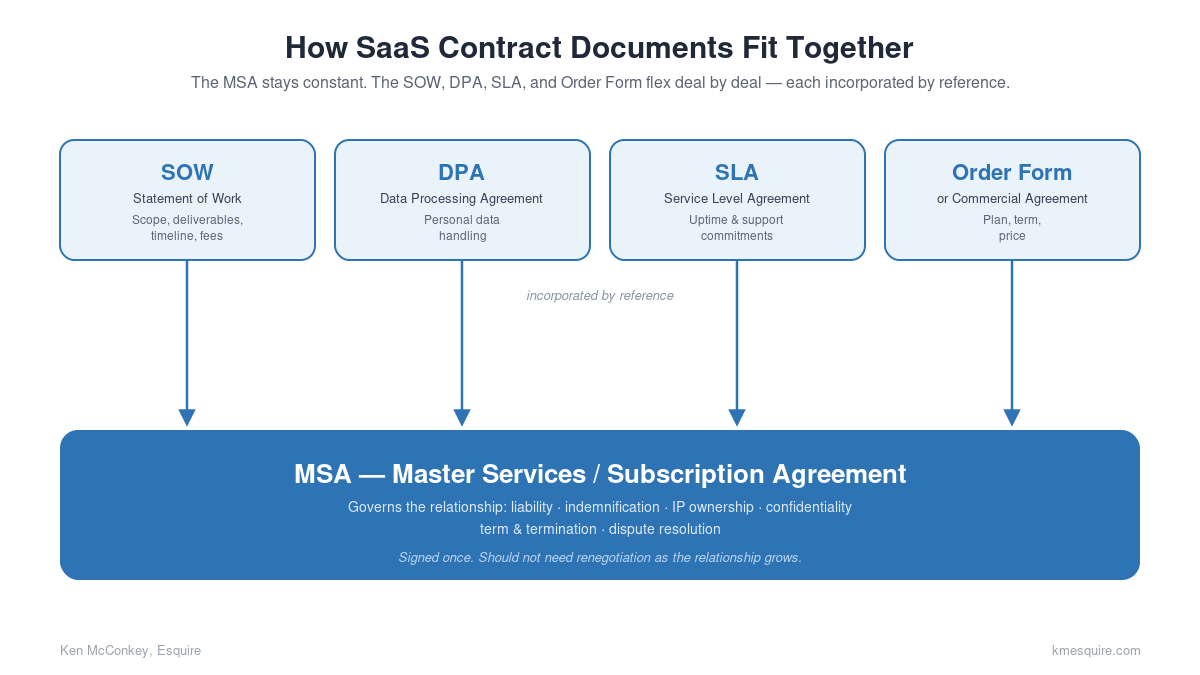
    Most SaaS companies eventually end up with some combination of a Master Services or Subscription Agreement (“MSA”) and a Statement of Work (“SOW”), often without ever deciding on purpose which document is supposed to do what. That usually happens by accident: an early customer needed a signed contract fast, so a single document covered everything, and each deal since has been a variation on that first one. It works until it doesn’t, usually right when a dispute or a new professional-services engagement exposes the gaps. Some companies call the SOW an Order Form or Commercial Agreement. Still others designate an SOW for professional services only and use a separate Order Form or Commercial Agreement for product purchases or subscriptions. For simplicity, this post uses “SOW” to refer to all of these documents, regardless of what your company calls them.

    What an MSA Actually Does

    The MSA is the overall governing document for the relationship. It sets the terms that should stay constant across every engagement with a given customer: limitation of liability, indemnification, intellectual property ownership and license grants, confidentiality, term and termination, and terms dictating how disputes get resolved. It also incorporates or references other supporting documents that carry the operational detail, typically a Data Processing Agreement (“DPA”) for personal data handling and a Service Level Agreement (“SLA”) for uptime and support commitments. Once an MSA is signed, it should not need to be renegotiated every time the relationship changes (i.e. additional services/products are added, or a subscription is renewed, etc.).

    What an SOW Actually Does

    The SOW carries the deal-specific detail: scope of work, deliverables, timeline, fees, and any engagement-specific assumptions or acceptance criteria. A well-drafted SOW does not restate liability caps, indemnification, or IP ownership; it incorporates the MSA by reference and leaves those terms where they belong. That separation is what lets a SaaS company add a new project, a new module, or a new phase of implementation without reopening the entire contract.

    When You Need Both

    If the product involves a recurring subscription plus periodic professional services, onboarding, custom integration work, implementation, or training, you need both documents. The MSA governs the relationship and the risk allocation; each SOW governs a discrete piece of work under that umbrella. This structure lets you sign a new SOW in days instead of weeks, because the terms that actually take time to negotiate are already settled.

    When a Single Order Form Is Enough

    Not every deal needs a freestanding SOW. A self-serve subscription with no custom implementation or professional services can often be handled with an MSA plus a short order form specifying the plan, term, and price. Reserve the full SOW structure for engagements that involve actual scoped work, deliverables, or a project timeline.

    Where SaaS Companies Typically Get Tripped Up

    Three recurring problems show up again and again:

    1. An SOW that includes its own liability or indemnification language that conflicts with the MSA, creating ambiguity about which terms actually control.
    2. An SOW signed for an early pilot or proof of concept with no MSA in place at all, so there is no governing framework once the relationship expands.
    3. No order-of-precedence clause specifying which document controls if the MSA and an SOW conflict, which turns a drafting oversight into a battle of contracts with no clearly stated winner. Most well-drafted MSAs default to the MSA controlling unless the SOW expressly says otherwise, so state that default in your own template rather than leaving it for a judge to decide.

    A Note on Execution

    All 50 states are covered by the federal ESIGN Act, and each state also has its own laws recognizing electronic signatures and records as legally effective, so executing MSAs and SOWs through AdobeSign, DocuSign or a similar platform is enforceable. However, that is not a substitute for good contract structure. A clean order-of-precedence clause and clear incorporation-by-reference language matter regardless of how the documents get signed.

    A Practical Starting Point

    Review your current templates for three things: a clear order-of-precedence clause, proper incorporation of the DPA and SLA by reference rather than restating their terms, and a standard SOW template that pulls its liability and IP terms from the MSA rather than reinventing them each time. Getting this structure right once saves renegotiation on every deal after.

    This post is provided for general informational purposes only and does not constitute legal advice. Reading this post does not create an attorney-client relationship. Contact ME to discuss your company’s specific contract structure.